Two Suspected TeamPCP Hackers Arrested in Australia Over Global Supply Chain Attacks
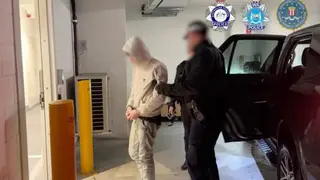
Australian police have arrested two men accused of participating in a hacking group that compromised over 1,000 organizations worldwide through a nine-month campaign. The arrests stem from a series of supply chain attacks that used a self-propagating worm to infect software packages and CI/CD pipelines. The suspects face 14 charges, though their names have not been officially released.
The arrests in Western Australia mark a significant law enforcement action against a group that has operated with unusual persistence since December. The suspects, residents of Cottesloe and Mandurah, face a combined 14 charges. Investigators reportedly benefited from the hackers' operational lapses, which security researchers noted were unusual for a group of their sophistication.
The group's Shai-Hulud worm exploited CI/CD pipelines to spread through software packages, with the Trivy scanner compromise serving as a notable infection vector that cascaded into downstream tools. The operation's use of Internet Computer Protocol-based canisters for command-and-control demonstrated technical sophistication, though researchers suggested AI tools may have compressed the learning curve for such advanced techniques.
The compromise of widely used developer tools could have far-reaching effects on software supply chains. Organizations that relied on affected packages may face credential theft and data exposure, potentially impacting customers and partners downstream. The arrests may deter similar groups, though the