AI-Voting Malware CLOSEDQUORUM Targets Credentials and Wallets
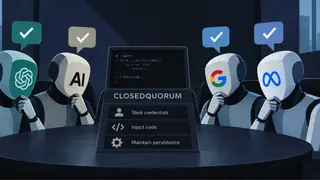
A Windows malware called CLOSEDQUORUM uses up to four AI models to vote on its actions instead of relying on a command server. It can steal Windows credentials, saved browser passwords, and crypto wallet data. Cisco Talos reported that the public version is non-functional and the full chain hasn't been observed.
The CLOSEDQUORUM malware represents an unusual design choice: instead of phoning home to a command-and-control server, it reportedly consults up to four AI models to decide its next moves. According to Cisco Talos, the publicly available version is non-functional, and the complete attack chain has not yet been observed in the wild. Its stated targets include Windows credentials, saved browser passwords, and cryptocurrency wallet data, suggesting a focus on credential theft and financial gain. This approach could complicate detection, as the malware’s behavior may vary based on AI responses rather than fixed instructions. However, without a working sample, its real-world effectiveness remains unproven.
If CLOSEDQUORUM or similar AI-driven malware matures, it could shift how defenders think about threat hunting—since no central server means fewer network indicators to block. Individuals using Windows devices with saved passwords or crypto wallets may face elevated risk if such tools become operational. Security teams could need new detection methods that account for unpredictable, AI-influenced actions. Yet, because the public build is broken and the full chain is unseen, immediate impact is likely limited, though the concept signals a possible evolution in malware autonomy.