AI Lowers the Cost of Retrying Failed Attacks, Reshaping SOC Work
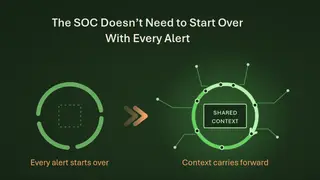
The article argues that AI's more immediate effect on security is making failed attacks inexpensive to repeat. It describes an attacker who gains a low-privilege cloud account and can quickly retry privilege escalation after an initial failure. This shifts the burden on security operations teams, which must handle repeated attempts without starting over each time.
The article points to a change in the economics of intrusion attempts: AI can make an unsuccessful effort easy to try again. After obtaining limited access in a cloud setting, an attacker may quickly make another attempt at higher privileges. Defenders then face recurring activity tied to the same incident. Security operations centers must handle these repetitions while maintaining continuity, rather than beginning anew each time. This operational strain is the piece's main focus.
If unsuccessful attacks become inexpensive to repeat, organizations using cloud services may see more persistent probing. Security teams could devote more attention to separating routine retries from genuine threats, which may affect response times and workload. Customers and employees whose data resides in those systems could be indirectly affected if defenses are stretched. The wider impact may depend on how well security operations adapt their processes and tools to repeated attempts.