Public Wi-Fi Threats Reassessed as Encryption Becomes Standard
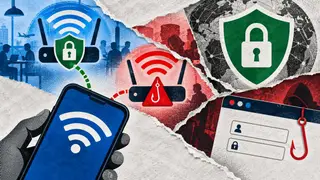
Most top websites now use HTTPS, and Chrome data shows encrypted browsing has become dominant since 2015. The FTC says public Wi-Fi is generally safe because of this encryption, but attacks above the transport layer still matter. A 2025 Perth case involved an evil twin network that stole credentials through a fake portal, and standards flaws such as SSID confusion remain a concern.
Encryption now covers nearly all leading websites: Internet Society Pulse puts HTTPS at 96% of the global top 1,000, while TLS 1.3 reaches 88%. Chrome telemetry shows encrypted navigation rising from roughly 30–45% in 2015 to 95–99% around 2020, then flattening. Regional HTTPS varies widely, from 65% in Asia to 93% in Oceania.
Even so, risk has shifted upward. A 2025 Perth evil twin case used a fake portal to capture log-in credentials without breaking encryption. Standards issues like SSID confusion (CVE-2023-52424) remain, and WiGLE data shows 1.83% of cataloged networks unencrypted and 2.50% still using WEP.
People using public hotspots in cafes, airports, hotels, and similar venues could benefit as encrypted browsing becomes the norm, reducing casual snooping. Yet those visiting legacy or private HTTP sites may still face credential theft or local-network attacks, as the Perth case suggests. Browser makers and network operators may face pressure to improve trust cues and fix standards weaknesses. The broader shift could lower opportunistic risk while leaving targeted, above-transport attacks as a persistent concern.