Widespread npm Package Supply Chain Attack Hijacks Developer WhatsApp Accounts
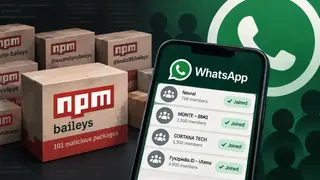
Researchers identified 101 compromised packages in the npm repository designed to automatically enroll developers into WhatsApp groups without authorization through an operation called PhantomSub. The malicious packages exploit the open-source Baileys WhatsApp library to execute the unauthorized account additions during installation. This discovery highlights persistent vulnerabilities in the software dependency supply chain where attackers target the development community for bulk account manipulation.
The PhantomSub operation represents a targeted assault on the development community through a vector that reaches engineers at a foundational stage of their work. By embedding malicious code within packages hosted on npm—a central repository relied upon by millions of developers—attackers gained access to systems during the installation process, when defenses are typically minimal. The use of the Baileys library, a legitimate tool for WhatsApp automation, demonstrates how attackers leverage existing open-source infrastructure to obscure their intentions.
Supply chain compromises of this scale underscore a critical challenge in modern software development: the difficulty of monitoring and verifying the trustworthiness of thousands of interconnected dependencies. The discovery of 101 compromised packages suggests a systematic effort rather than isolated incidents, pointing to gaps in both npm's detection mechanisms and developers' ability to vet third-party code before integrating it into projects.
This attack could impact developers whose systems were compromised during package installation, potentially exposing their WhatsApp accounts and contact networks to unauthorized access. Organizations relying on these packages may face ripple effects across their supply chains. The incident may drive discussions about enhanced verification protocols for package repositories and increased scrutiny of dependencies, though the practical implementation of comprehensive vetting at scale remains challenging given the volume of code flowing through open-source ecosystems.