Threat Actors Hijack ChatGPT Custom GPTs to Distribute Remote Access Trojans
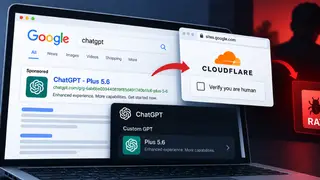
Attackers are creating fraudulent ChatGPT Custom GPTs that impersonate legitimate products and redirect victims to malicious websites deploying ClickFix social engineering tactics to deliver remote access trojans. Huntress researchers identified this activity in late September 2026, marking an escalation in the abuse of trusted AI platform features for malware distribution. This campaign demonstrates how adversaries are repurposing AI tools to enhance the credibility of their phishing attacks.
Researchers at Huntress discovered a malicious campaign in late September 2026 in which bad actors established unauthorized Custom GPTs mimicking well-known software products. These fraudulent applications functioned as entry points, steering unsuspecting users toward compromised websites. Once users arrived at these sites, they encountered ClickFix techniques—a social engineering method designed to manipulate victims into taking actions that compromise their systems.
The malware ultimately deployed through this chain of deception is classified as remote access trojans, tools that grant attackers unauthorized control over infected machines. This discovery underscores how established, trusted platforms can become vectors for sophisticated attacks when threat actors exploit their legitimacy.
This activity could significantly impact both individual users and organizations relying on generative AI tools for productivity. Users may face heightened risk if they cannot reliably distinguish authentic applications from counterfeits, potentially leading to data breaches or system compromise. Enterprises could see downstream effects through compromised employee devices. The incident may prompt platforms to strengthen verification mechanisms and raises questions about how AI services can better protect users from impersonation without restricting legitimate use.