CloudSyncD Infostealer Exploits Zoom Installer Disguise to Target Mac Users
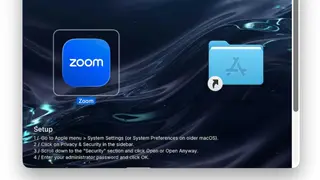
Security researchers at Jamf Threat Labs have uncovered new malware that poses as a legitimate Zoom installer while secretly installing CloudSyncD, an information-stealing tool that captures user data and sends it to attackers. The malware bypasses macOS Gatekeeper protections by including visual instructions that trick users into overriding security features. CloudSyncD operates silently in the background and can transmit stolen data every 8 seconds while also executing remote commands for attackers.
Security researchers identified a sophisticated distribution method where attackers bundle legitimate Zoom software alongside malicious code. The threat exploits a common macOS installation pattern—dragging applications into the Applications folder—to gain user trust while circumventing built-in protections through deceptive on-screen guidance that instructs victims to manually disable Gatekeeper security warnings.
Once installed, CloudSyncD operates covertly to harvest sensitive user information and transmit it at extremely frequent intervals. The malware's dual-purpose design allows attackers not only to steal data but also to remotely control compromised systems, creating an ongoing threat rather than a one-time compromise.
This threat could particularly affect Mac users who download software from unofficial channels or inadvertently bypass security warnings. Organizations with macOS-based workforces may face data breaches if employees install compromised applications, potentially exposing confidential business information. The incident may prompt renewed user awareness about installation sources and security dialogs, though it could also increase support requests as users become more cautious about system warnings.