Google Restricts Accessibility API Access in Android 17 to Combat Malware Threats
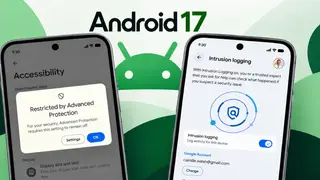
Google introduced a security enhancement in Android 17 that restricts accessibility service permissions to only verified accessibility tools when Advanced Protection mode is active. This restriction targets a critical vulnerability where malicious applications have exploited the accessibility API to distribute malware and conduct financial fraud. The measure aims to eliminate a significant attack vector that cybercriminals have routinely used to compromise Android devices.
Google's latest operating system update implements stricter controls over which applications can utilize accessibility features on Android devices. Accessibility services, originally designed to assist users with disabilities by enabling alternative navigation methods, have become a preferred exploitation method for threat actors seeking unauthorized device control. By limiting permission grants to only certified accessibility tools during Advanced Protection mode activation, the company aims to reduce exposure to this particular compromise technique.
This vulnerability has proven especially attractive to criminals pursuing financial gain, as accessibility APIs grant broad system-level permissions that can intercept user interactions and data. The restriction represents a defensive response to widespread malware campaigns that have leveraged these capabilities to steal credentials and execute unauthorized transactions on compromised devices.
The change could provide meaningful security improvements for users who enable Advanced Protection mode, particularly those managing sensitive financial accounts or handling confidential information. Device manufacturers and accessibility software developers may experience workflow adjustments, though verified tools would retain functionality. Android users with disabilities relying on legitimate accessibility applications should see continued support, while cybersecurity professionals may view this as a necessary control point in reducing attack surface complexity across the platform.