Attackers Weaponize Realtek SDK Flaw to Deploy Botnet Using Novel C2 Protocol
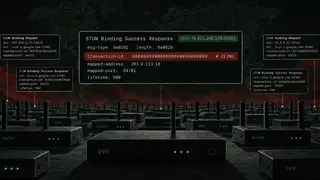
Threat actors are actively exploiting a patched critical vulnerability in the Realtek Jungle SDK to deploy the Cling botnet malware across compromised systems. The Cling malware distinguishes itself by repurposing standard STUN protocol behavior as a command-and-control communication channel, allowing attackers to maintain persistence and control over infected devices. Security researchers warn that organizations running unpatched Realtek components remain at immediate risk.
A critical vulnerability within Realtek's Jungle SDK has become the target of active exploitation campaigns. Threat actors have leveraged this flaw to distribute Cling, a botnet designed to establish control over vulnerable devices and maintain long-term access to compromised infrastructure.
The malware's technical sophistication lies in its command infrastructure. Rather than relying on conventional control mechanisms, attackers have adapted the STUN protocol—typically used for network connectivity purposes—to serve as a covert channel for issuing commands and receiving data from infected systems. This approach obscures malicious traffic within legitimate protocol usage, complicating detection efforts for network defenders.
Organizations deploying Realtek components face significant operational risks if patches remain unapplied. Unpatched systems could become entry points for botnet infections, potentially exposing networks to data exfiltration, lateral movement, and resource hijacking. Device manufacturers, system administrators, and end users relying on affected Realtek technology may need to prioritize urgent patching cycles to mitigate exposure, though broader impact depends on the prevalence of vulnerable deployments across consumer and enterprise environments.