Threat Actors Deploy Phishing Platform Impersonating AI Chatbot Ad Services
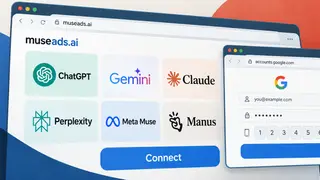
Researchers uncovered a sophisticated phishing operation that creates fraudulent advertising portals mimicking legitimate services for popular AI chatbots including ChatGPT, Gemini, and Claude. These fake platforms trick users into entering their login credentials and multi-factor authentication codes under the guise of offering campaign management and business account features. The scheme targets users seeking to optimize advertising spend across multiple AI service providers.
Phishing campaigns have evolved to exploit the growing commercial interest in artificial intelligence platforms. By designing fake portals that replicate the appearance of legitimate advertising management tools, threat actors are capitalizing on businesses' desire to streamline their marketing efforts across multiple AI services simultaneously. This particular operation demonstrates how fraudsters leverage the trust users place in established technology brands to compromise account security at scale.
The attack specifically targets the credential entry point, a moment when users are focused on accessing services rather than verifying authenticity. By requesting both standard login information and multi-factor authentication codes, attackers gain sufficient access to potentially compromise associated accounts and sensitive business data, underscoring how even security-conscious users can be deceived through sophisticated social engineering.
This phishing scheme could expose business users to account takeovers, unauthorized access to advertising accounts, and potential financial losses through fraudulent spending. Marketing professionals and small-to-medium enterprises managing ad campaigns may face particular vulnerability, as they often juggle credentials across multiple platforms. The incident illustrates how AI's mainstream adoption creates new attack surfaces, potentially affecting broader user confidence in managing legitimate AI tools for business purposes.