Registry Breaches in Three ccTLDs Enabled Rogue HTTPS Certificates for Google Domains
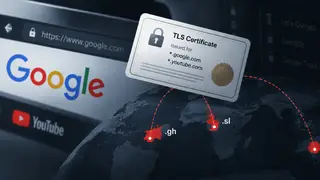
Google reported that attackers took over registry infrastructure for Ghana, Sierra Leone, and American Samoa top-level domains and used it to issue unauthorized TLS certificates for some Google domains. Google's own systems were not compromised, but domains under .gh, .sl, and .as were affected. Such certificates could allow an adversary to impersonate legitimate encrypted websites.
This report points to a broader trust problem in encrypted web browsing: certificates are meant to confirm that a site is genuine, but their issuance can be abused when domain registry systems are taken over. According to Google, attackers gained control of registry operations for three country-code top-level domains—Ghana’s .gh, Sierra Leone’s .sl, and American Samoa’s .as—and then obtained certificates for certain Google domains without authorization. Google said its own systems remained secure. The domains involved fall under those three ccTLDs. The case shows how a compromise outside a company’s own network can still affect certificate trust.
The reported breach could affect people and