Exploit Released for AnyDesk Linux Flaw Allowing Root Access Before Authentication
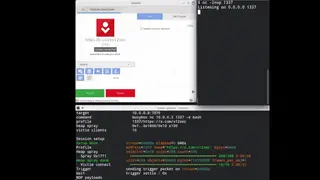
Security researchers have published a working exploit for a pre-authentication remote code execution bug in AnyDesk's Linux client. The vulnerability can give an attacker root privileges before a connection is approved. AnyDesk addressed the issue in version 8.0.3 in June, but the release notes only mentioned a crash fix, and no CVE was assigned.
Security researchers have made public a functioning exploit for a flaw in AnyDesk’s Linux client. The issue is a pre-authentication remote code execution bug, meaning an attacker could obtain root access before a connection is approved.
AnyDesk fixed the problem in version 8.0.3 in June. However, the release notes for that version mentioned only a crash fix, and no CVE identifier was assigned to the vulnerability.
Organizations and individuals running AnyDesk on Linux may be affected. Because the flaw can be exploited before authentication, attackers could gain root-level control of reachable systems, potentially enabling data theft, service disruption, or further network compromise. The absence of a CVE and limited release-note detail may make it harder for defenders to track and prioritize patching. Remote-access tools are widely used, so even a narrow platform-specific bug could have outsized operational consequences if left unaddressed.