CISA Adds Five Flaws to KEV Catalog After Flax Typhoon Attacks
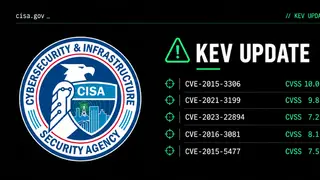
CISA added five vulnerabilities to its Known Exploited Vulnerabilities catalog after a China-linked group called Flax Typhoon abused them. Federal agencies were given an October 11 deadline to address the flaws. The list includes CVE-2015-3306, a critical improper access control issue in ProFTPD.
Expanded Detail
EXPANDED:
CISA's Known Exploited Vulnerabilities catalog is used to flag flaws that attackers have already exploited, prompting federal agencies to remediate them by a set deadline. In this case, five vulnerabilities were added after attacks by Flax Typhoon, described as a China-linked group. The list includes CVE-2015-3306, a critical access-control flaw in ProFTPD.
Expanded detail and Context are AI-generated analysis; the linked article remains the authoritative source.
Related stories
OT Security Briefing Covers Federal Guidance and Vendor Fixes · Cybersecurity
This summary is Al-enhanced to contain extended analysis and broader social context. The original is {NAME); the linked article is the authoritative source. Original headline: “Flax Typhoon Exploits Five Flaws as CISA Sets October 11 Deadline for Federal Agencies.” Browse more stories.