Compromised eMudhra Certificate Authority Keys Prompt Browser and Software Remediation
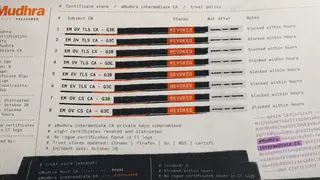
Mozilla and Chrome's Root Program confirmed on October 20 that private keys for eight eMudhra intermediate certificate authority certificates had been exposed. Since intermediate CAs issue website certificates, anyone with one of these keys could create browser-trusted certificates for arbitrary sites. A researcher reported the issue, leading to emergency fixes.
The disclosure centered on private keys for eight eMudhra intermediate certificate authority certificates, according to Mozilla and Chrome’s Root Program on October 20. Because intermediate CAs issue certificates for websites, anyone holding one of the exposed keys could potentially create certificates that browsers would trust for arbitrary sites. A researcher reported the issue, and the response involved emergency fixes. The episode illustrates the trust-chain problem at the heart of secure browsing: browser programs and certificate authorities must act quickly when a key that underpins website authentication is no longer assumed private.
The exposure could affect ordinary web users, site operators, and organizations that depend on browser-trusted certificates, because confidence in the certificate chain may be weakened until remediation is confirmed. Browser makers and certificate authorities may need to update trust decisions or replace affected certificates, and users could encounter warnings or service disruptions. The wider societal impact depends on how quickly fixes are completed and whether any misuse occurred, which the available summary does not establish.