Public Exploit Code Released for Severe FortiSIEM Remote Code Execution Vulnerability
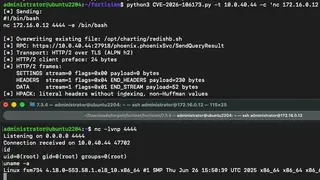
Security researchers have published proof-of-concept exploit code for a critical FortiSIEM vulnerability that has already been patched. The flaw, tracked as CVE-2026-106173 with a CVSS score of 9.4, is a path traversal issue that can let an unauthenticated attacker run arbitrary code or commands.
The FortiSIEM vulnerability is tracked as CVE-2026-106173 and has a CVSS score of 9.4, marking it as severe. It is a path traversal issue that can let an unauthenticated attacker run arbitrary code or commands.
Security researchers have published proof-of-concept exploit code for the flaw. The vulnerability has already been patched.
Organizations using FortiSIEM could face increased risk if affected systems remain unpatched, since public exploit code may make the flaw easier to test or misuse. Security teams may need to prioritize patch verification and monitoring. Indirect effects could reach users and partners if compromised systems disrupt services or expose sensitive information. The severity score suggests the issue warrants prompt attention, though actual impact depends on exposure and deployment.