Mass Exploit Attempts Target PHP2Shell Flaws to Spread Mirai Variant
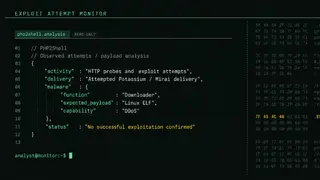
Attackers have been trying to use newly revealed PHP2Shell flaws to infect systems with a Mirai variant called Potassium, but the attempts have not succeeded. The vulnerabilities are rated 9.2 and could permit remote code execution without authentication.
Recently disclosed PHP2Shell vulnerabilities carry a 9.2 severity rating and could let an attacker run code remotely without credentials. According to the summary, attempts to use these flaws to deploy Potassium, a Mirai variant, have not succeeded. The case illustrates how newly public security gaps can quickly attract malware activity, even when early exploitation efforts fail.
Organizations running systems affected by the PHP2Shell flaws could face heightened risk if exploitation succeeds, potentially disrupting services or exposing data. Because the reported attempts have not succeeded, immediate broad impact may be limited, but administrators may still need to prioritize patching and monitoring. The public could be affected indirectly if compromised devices are later used in malware networks, though the summary does not confirm that outcome.